

Cybersecurity in Slovakia: How to Protect Against Growing Threats?
30. marca 2025
Cybersecurity is currently a very important topic, especially in Slovakia. In recent months, the country has experienced an increased number of cyber attacks. The average record shows that organizations in the country faced approximately 1,443 attacks weekly. These attacks, which are often automated, use robotic tools to test vulnerabilities.
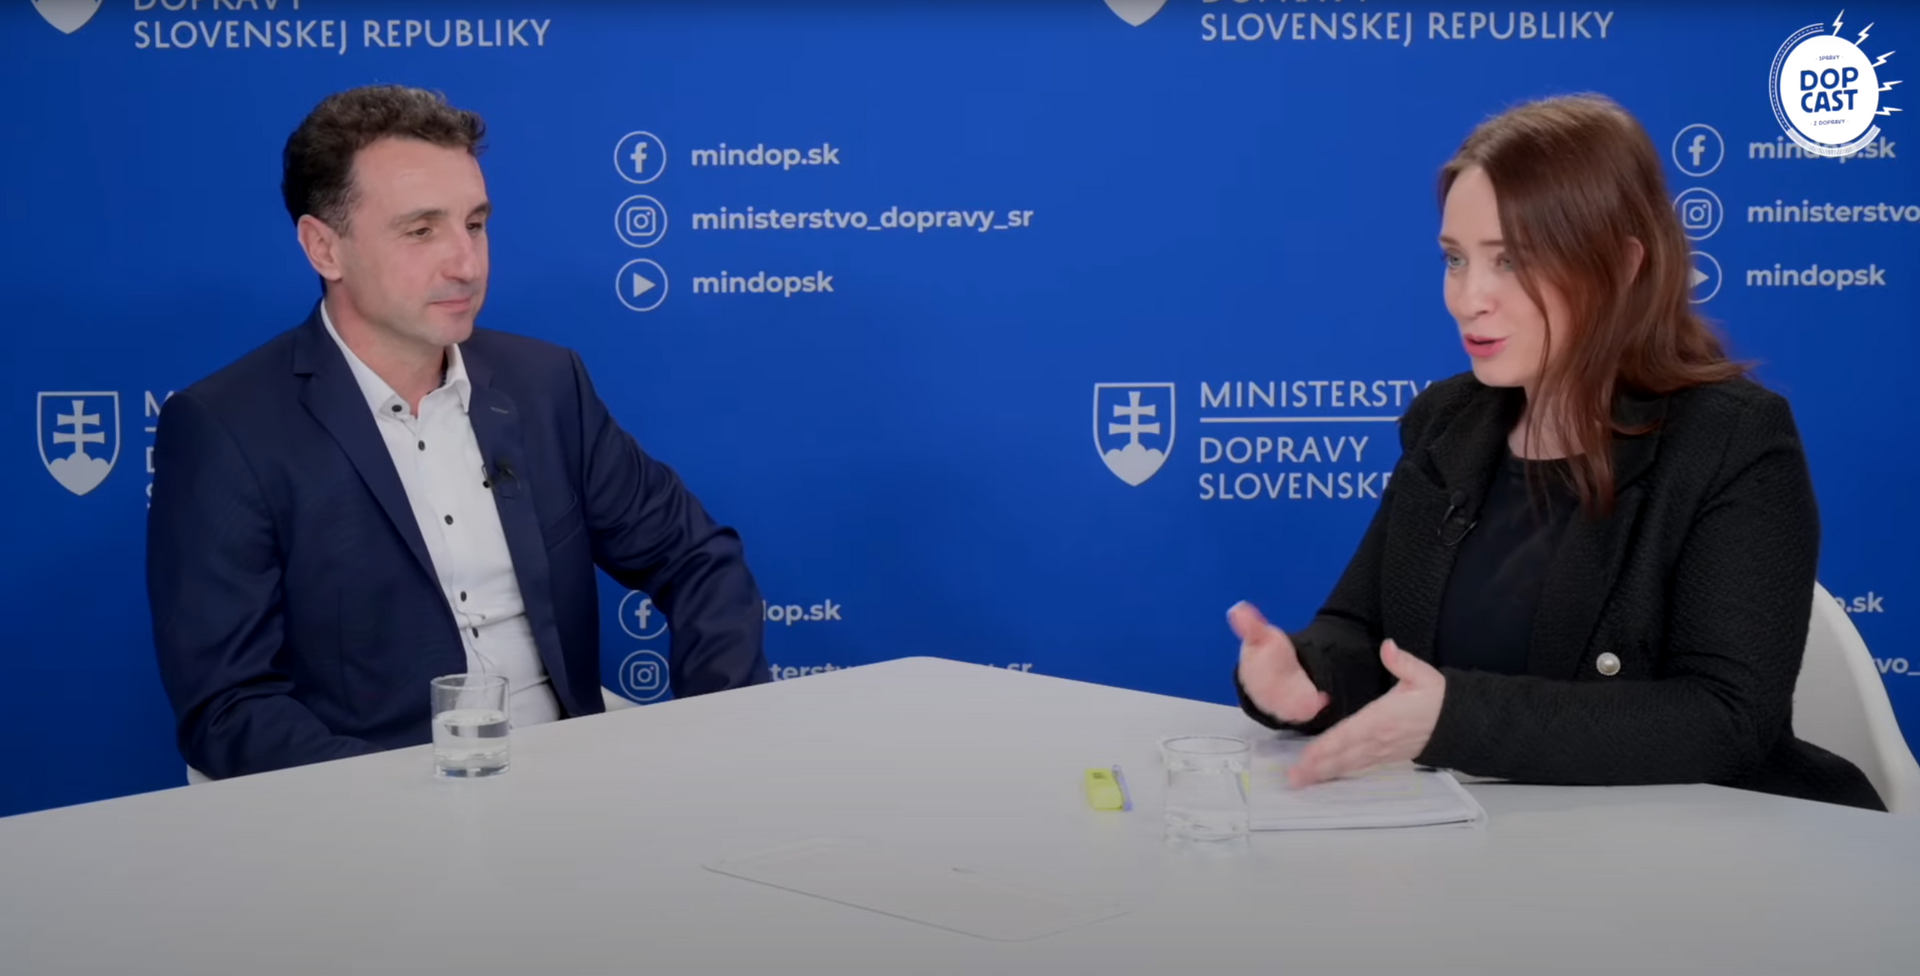
In discussion about these attacks, the need for protection and security against such threats also emerges. Various companies, from small businesses to large corporations, must take the protection of their data seriously. Cybersecurity representatives warn that attacks can lead not only to financial losses but also to damage to the reputation and credibility of organizations.
Slovakia faces thousands of cyber attacks weekly. Data protection is essential for business operations. Cybersecurity requires compliance with legislation and regulations.
Statistics and Vulnerabilities
In the last six months, Slovakia has recorded an average of 1,443 cyber attacks per week on one organization. These attacks are mostly automated, with attackers using various robotic tools and botnets to test system vulnerabilities. The attackers' primary goal is to obtain money or sensitive data that can be subsequently misused.
The profit from these attacks can include not only financial resources but also obtaining personal or business information. If an attack occurs, organizations often lose credibility and reputation by being unable to secure their employees' or clients' data protection.
Types of Attacks and Criminal Objectives
Cybercriminals target various organizations and use diverse methods. Common attack types include ransomware - where attackers encrypt data and demand ransom to unlock it. Phishing is an attempt to obtain confidential information through fraudulent emails. DDoS attacks overload servers to disrupt services.
Importantly, all organizations, regardless of size, are potential targets. Organizations can lose money, data, or even the trust of their clients, which has long-term negative consequences.
Reputation and Data Protection
Slovakia encounters a high number of cyber attacks, averaging 1,443 per week for one organization. These attacks are often automated and focus on testing vulnerabilities. Attackers have various objectives, including obtaining sensitive information such as employees' and clients' personal data.
It is crucial for organizations to protect their reputation and data. Information misuse can lead to loss of credibility and image, which is particularly serious for companies processing large volumes of personal data. For example, if a company were to change banks and an attacker sent a false email, it could cause significant damage to all involved parties.
Prevention and Remedial Measures
To protect against cyber threats, strong security is necessary. International guidelines like NIS2 create a framework for cybersecurity. Each state must adapt the requirements of these guidelines to its own legal regulations.
Slovak cybersecurity laws may differ from other countries, but their implementation was one of the best in Europe. Companies should regularly update their security procedures and employee training to prevent attacks and ensure data protection.
Comparison with Other Countries
Slovakia encounters an average of 1,443 cyber attacks weekly per organization. Attackers within these attacks often use automated systems that examine vulnerabilities in organizations. Every country faces cyber threats, but attack intensity varies. For example, in more developed countries like Germany and the United States, identity theft is much more common than in Slovakia.
Additionally, countries differ in their approaches to data protection and cybersecurity. In Slovakia, even though attacks are not as frequent, it is important for organizations to secure themselves against risks. Identity and well-managed data are key to protecting company reputations.
International Cooperation
The European Union attempts to unify cybersecurity approaches through the NIS 2 directive. Each country must adapt its laws according to this directive, leading to different implementations across states. Slovakia has a reputation for good transposition of this directive, which helps improve its cybersecurity.
By cooperating with other member states, Slovakia can share information and experiences, which strengthens collective defense against cyber threats. Given developments, Slovakia should remain flexible and current concerning new standards like NIS 3, which come with new requirements and norms.
NIS Directive and National Law Transposition
Europe introduced the NIS directive, which was replaced by an improved NIS 2 version. This measure is important for protection against cyber threats. Each state must create its own law that reflects NIS 2 directive requirements into national law. This means the Slovak cybersecurity law will differ from those in other countries like the Czech Republic or Austria.
The NIS 2 directive provides a framework for cybersecurity in the EU. Each member state must submit its own law, with Slovak transposition being among the best in Europe.
Updates and Legal Norm Expansion
The NIS 2 directive expanded the number of organizations that must comply with security measures. Previously, this did not apply to manufacturing companies like automotive manufacturers, which are very significant in Slovakia. Currently, protection steps are needed in these sectors.
Key changes in NIS 2: more organizations are subject to regulation, industry specifics are considered (like the automotive sector), planned NIS 3 directive updates for adaptation to new threats.
Manufacturing and Automotive Sector
In Slovakia, cyber attacks also affect the manufacturing sector, primarily the automotive industry. This sector is one of the most significant in the country. Approximately 200 companies are involved in the manufacturing chain. These companies employ a large number of people and process numerous sensitive data.
Automobile manufacturers and suppliers are often targets of automated attacks. These attacks attempt to gain access to sensitive information or disrupt production processes. Attackers focus on system vulnerabilities to obtain financial or other advantages.
Consequences for Medium and Large Enterprises
Medium and large enterprises in the automotive industry face serious challenges due to cyber threats. Attack consequences can lead to loss of customer credibility and trust. When a security breach occurs, companies must face reputation damage, which can have long-term effects on their trading.
Moreover, companies must invest in protection against such threats. This can include implementing new technologies and training employees in cybersecurity. Although protection costs can be high, prevention of cyber attacks is essential for maintaining stability and success in this growing industry.
Upcoming Tools and Innovations
Slovakia faces frequent cyber attacks. On average, this involves 1,443 attacks weekly per organization. These attacks are mostly automated, with botnets testing system vulnerabilities. Attackers aim to obtain valuable data, money, or gain system control. Attacks can take various forms, including data encryption and ransom demands.
Organizations becoming victims lose credibility. Even small companies managing employee and client personal data are at risk. It is important to be aware of these factors and secure against potential threats.
European directives like NIS 2 define cybersecurity requirements. Each state implements these requirements differently, leading to diversity in regulations. New regulations expand obligations to the manufacturing sector, including automotive manufacturers.
New tools and approaches to threat protection are also being prepared. This process is essential for organizations to stay safe from continuously evolving cyber threats.
Source: Ministerstvo dopravy SR. 2025. “DOPRAVA BUDE BEZPEČNEJŠIA.” YouTube, March 23, 2025. https://www.youtube.com/watch?v=NrbPAns7o5A. Accessed: 27. 3. 2025
Cyber Attacks in Slovakia
Statistics and Vulnerabilities
In the last six months, Slovakia has recorded an average of 1,443 cyber attacks per week on one organization. These attacks are mostly automated, with attackers using various robotic tools and botnets to test system vulnerabilities. The attackers' primary goal is to obtain money or sensitive data that can be subsequently misused.
The profit from these attacks can include not only financial resources but also obtaining personal or business information. If an attack occurs, organizations often lose credibility and reputation by being unable to secure their employees' or clients' data protection.
Types of Attacks and Criminal Objectives
Cybercriminals target various organizations and use diverse methods. Common attack types include ransomware - where attackers encrypt data and demand ransom to unlock it. Phishing is an attempt to obtain confidential information through fraudulent emails. DDoS attacks overload servers to disrupt services.
Importantly, all organizations, regardless of size, are potential targets. Organizations can lose money, data, or even the trust of their clients, which has long-term negative consequences.
Securing Against Cyber Threats
Slovakia encounters a high number of cyber attacks, averaging 1,443 per week for one organization. These attacks are often automated and focus on testing vulnerabilities. Attackers have various objectives, including obtaining sensitive information such as employees' and clients' personal data.
It is crucial for organizations to protect their reputation and data. Information misuse can lead to loss of credibility and image, which is particularly serious for companies processing large volumes of personal data. For example, if a company were to change banks and an attacker sent a false email, it could cause significant damage to all involved parties.
Prevention and Remedial Measures
To protect against cyber threats, strong security is necessary. International guidelines like NIS2 create a framework for cybersecurity. Each state must adapt the requirements of these guidelines to its own legal regulations.
Slovak cybersecurity laws may differ from other countries, but their implementation was one of the best in Europe. Companies should regularly update their security procedures and employee training to prevent attacks and ensure data protection.
Global Cybersecurity Context
Slovakia encounters an average of 1,443 cyber attacks weekly per organization. Attackers within these attacks often use automated systems that examine vulnerabilities in organizations. Every country faces cyber threats, but attack intensity varies. For example, in more developed countries like Germany and the United States, identity theft is much more common than in Slovakia.
Additionally, countries differ in their approaches to data protection and cybersecurity. In Slovakia, even though attacks are not as frequent, it is important for organizations to secure themselves against risks. Identity and well-managed data are key to protecting company reputations.
International Cooperation
The European Union attempts to unify cybersecurity approaches through the NIS 2 directive. Each country must adapt its laws according to this directive, leading to different implementations across states. Slovakia has a reputation for good transposition of this directive, which helps improve its cybersecurity.
By cooperating with other member states, Slovakia can share information and experiences, which strengthens collective defense against cyber threats. Given developments, Slovakia should remain flexible and current concerning new standards like NIS 3, which come with new requirements and norms.
Regulations and Legislation
Europe introduced the NIS directive, which was replaced by an improved NIS 2 version. This measure is important for protection against cyber threats. Each state must create its own law that reflects NIS 2 directive requirements into national law. This means the Slovak cybersecurity law will differ from those in other countries like the Czech Republic or Austria.
The NIS 2 directive provides a framework for cybersecurity in the EU. Each member state must submit its own law, with Slovak transposition being among the best in Europe.
Updates and Legal Norm Expansion
The NIS 2 directive expanded the number of organizations that must comply with security measures. Previously, this did not apply to manufacturing companies like automotive manufacturers, which are very significant in Slovakia. Currently, protection steps are needed in these sectors.
Key changes in NIS 2: more organizations are subject to regulation, industry specifics are considered (like the automotive sector), planned NIS 3 directive updates for adaptation to new threats.
Industry Impact
In Slovakia, cyber attacks also affect the manufacturing sector, primarily the automotive industry. This sector is one of the most significant in the country. Approximately 200 companies are involved in the manufacturing chain. These companies employ a large number of people and process numerous sensitive data.
Automobile manufacturers and suppliers are often targets of automated attacks. These attacks attempt to gain access to sensitive information or disrupt production processes. Attackers focus on system vulnerabilities to obtain financial or other advantages.
Consequences for Medium and Large Enterprises
Medium and large enterprises in the automotive industry face serious challenges due to cyber threats. Attack consequences can lead to loss of customer credibility and trust. When a security breach occurs, companies must face reputation damage, which can have long-term effects on their trading.
Moreover, companies must invest in protection against such threats. This can include implementing new technologies and training employees in cybersecurity. Although protection costs can be high, prevention of cyber attacks is essential for maintaining stability and success in this growing industry.
Future of Cybersecurity
Slovakia faces frequent cyber attacks. On average, this involves 1,443 attacks weekly per organization. These attacks are mostly automated, with botnets testing system vulnerabilities. Attackers aim to obtain valuable data, money, or gain system control. Attacks can take various forms, including data encryption and ransom demands.
Organizations becoming victims lose credibility. Even small companies managing employee and client personal data are at risk. It is important to be aware of these factors and secure against potential threats.
European directives like NIS 2 define cybersecurity requirements. Each state implements these requirements differently, leading to diversity in regulations. New regulations expand obligations to the manufacturing sector, including automotive manufacturers.
New tools and approaches to threat protection are also being prepared. This process is essential for organizations to stay safe from continuously evolving cyber threats.
Source: Ministerstvo dopravy SR. 2025. “DOPRAVA BUDE BEZPEČNEJŠIA.” YouTube, March 23, 2025. https://www.youtube.com/watch?v=NrbPAns7o5A. Accessed: 27. 3. 2025
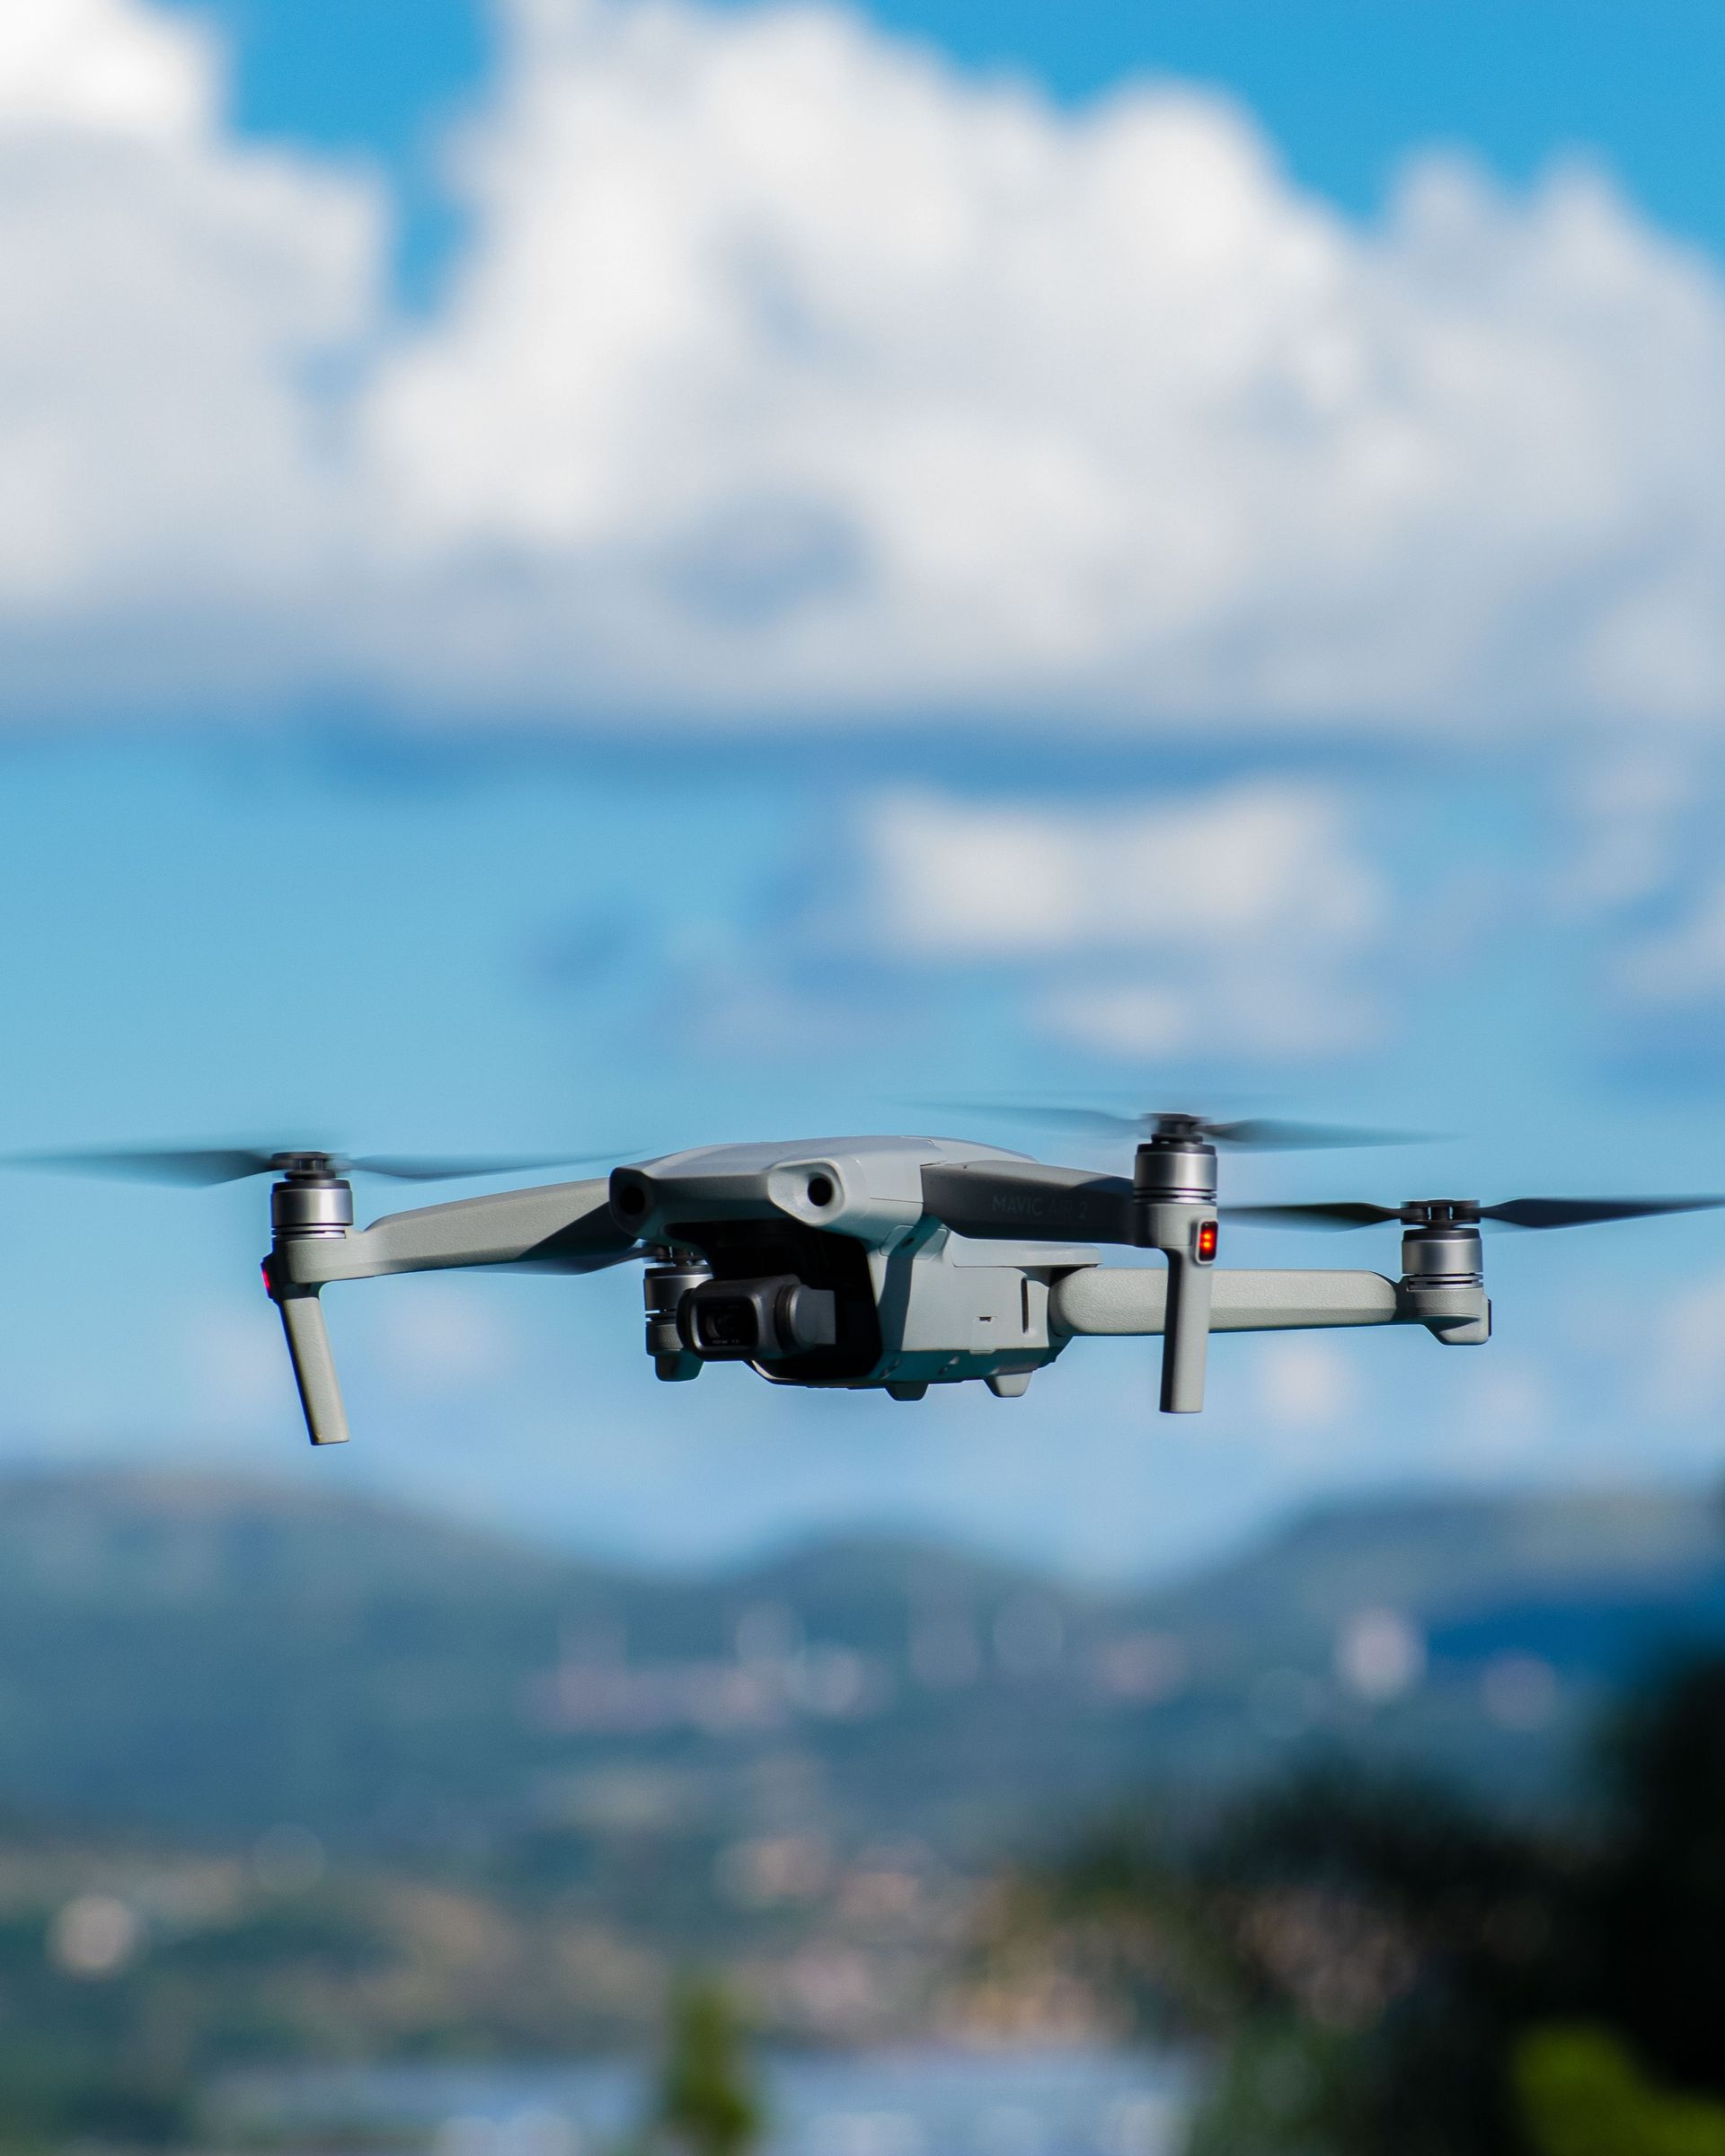
A drone flying over a power plant, airport or water facility does not have to cause any physical damage to disrupt its operations. It may be enough for it to appear in the wrong place at the wrong time, while the critical entity has no idea what it is doing there. This is precisely why attention in Europe is shifting from technologies designed to neutralise drones to something less visible: the ability of critical entities to detect an incident in time, assess it correctly and manage it without unnecessary losses.
Dron nad elektrárňou, letiskom alebo vodárenským objektom nemusí nič poškodiť, aby narušil jeho fungovanie. Stačí, že sa objaví v nesprávnom čase na nesprávnom mieste a kritický subjekt nevie, čo tam robí. Práve preto sa pozornosť v Európe presúva od samotných technológií na zneškodnenie dronov k niečomu menej viditeľnému: k schopnosti kritických subjektov incident včas zachytiť, správne vyhodnotiť a zvládnuť bez zbytočných strát.
A series of expert articles by the Critical Infrastructure Association of the Slovak Republic on essential services under Annex No. 1 to Act No. 367/2024 Coll. on Critical Infrastructure
Séria odborných článkov Asociácie kritickej infraštruktúry Slovenskej republiky o základných službách podľa prílohy č. 1 zákona č. 367/2024 Z. z. o kritickej infraštruktúre
The incident at the primary school in Staškov brings back a topic that deserves continuous attention, not just attention in the aftermath of an incident. The protection of soft targets should form part of a systematic security policy, with clearly defined measures, responsibilities and preparedness for various types of threats.
Udalosť v základnej škole v Staškove pripomína tému, ktorá si zaslúži pozornosť priebežne, nie až po incidente. Ochrana mäkkých cieľov by mala byť súčasťou systematickej bezpečnostnej politiky, s jasne nastavenými opatreniami, zodpovednosťami a pripravenosťou na rôzne typy hrozieb.
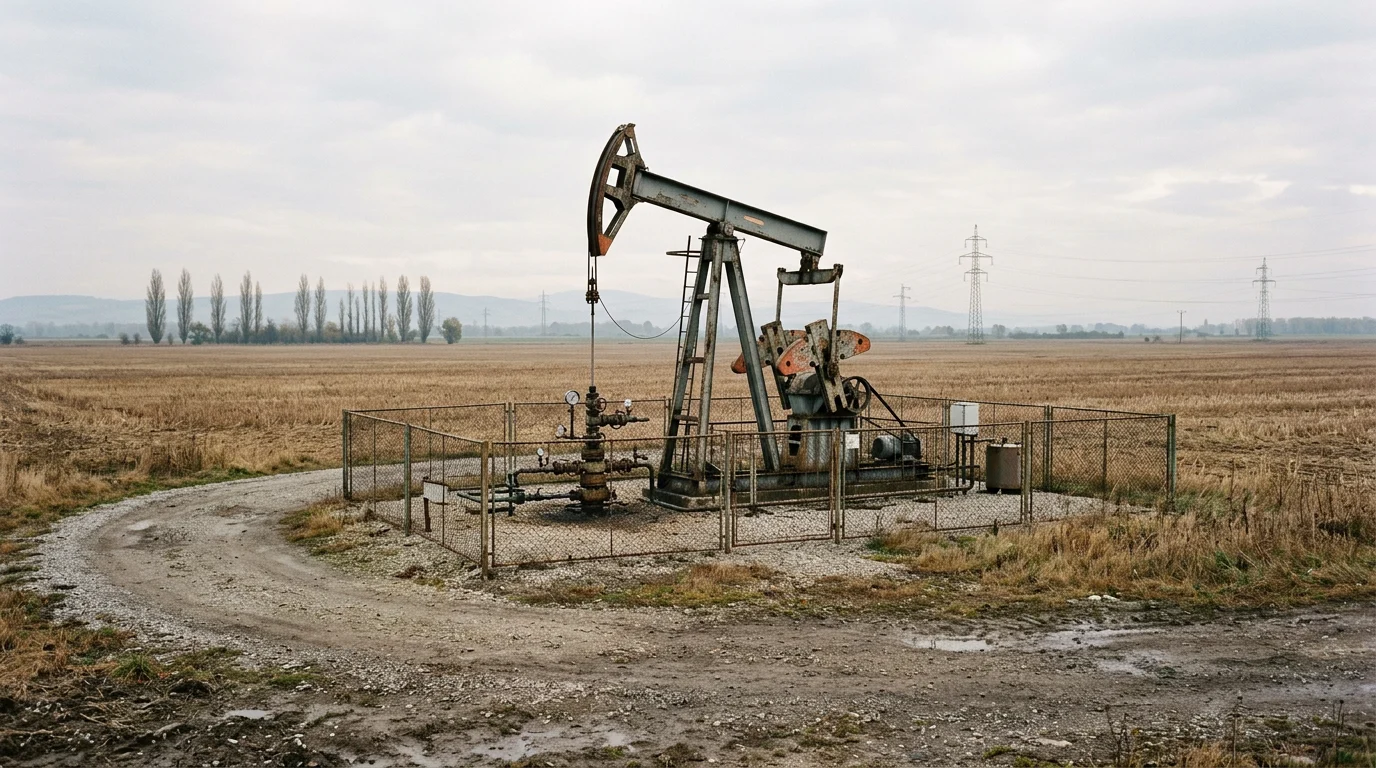
We are continuing the series of expert articles by the Critical Infrastructure Association of the Slovak Republic, in which we gradually introduce the individual essential services listed in Annex No. 1 to Act No. 367/2024 Coll. on Critical Infrastructure. Having covered the operation of pipelines for the transport of crude oil and motor fuels, today we move one step upstream to a service that stands at the very beginning of the entire oil chain: crude oil extraction.
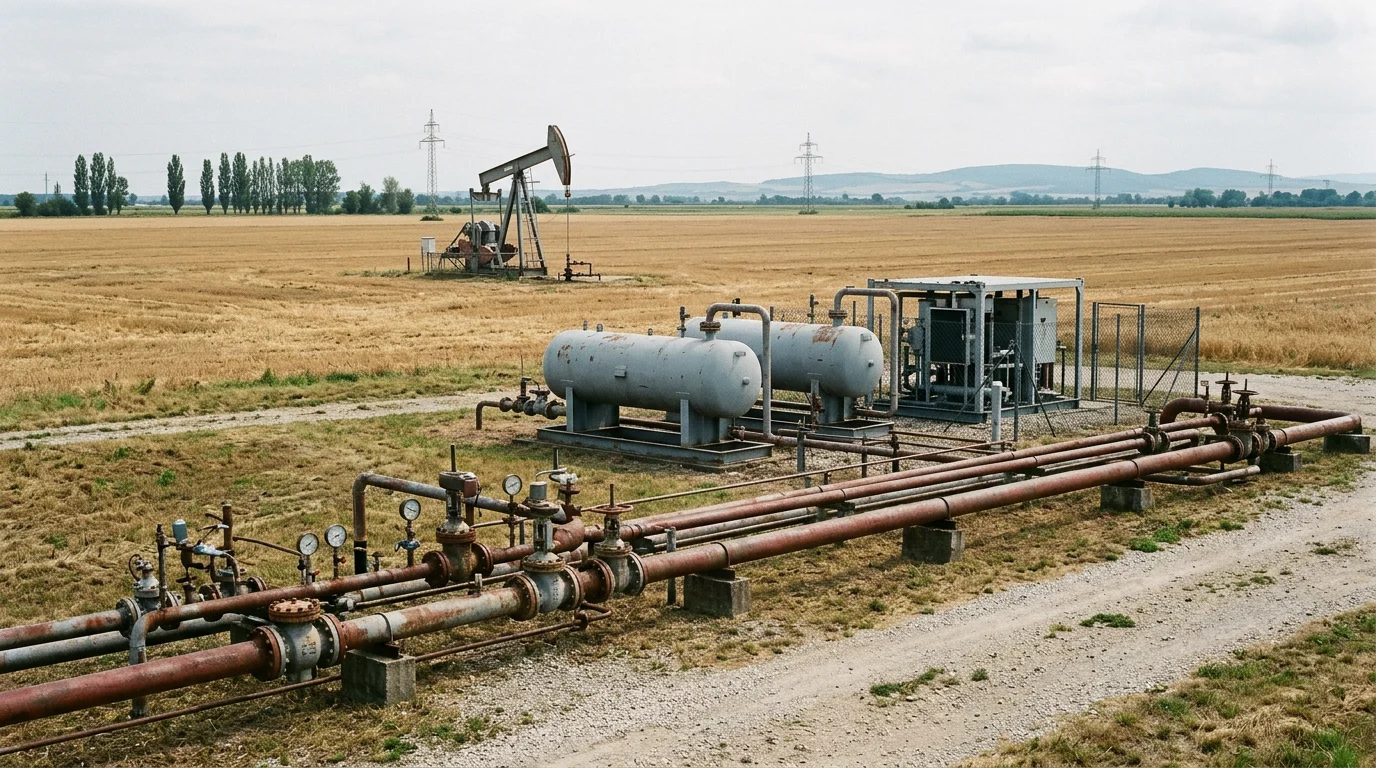
Pokračujeme v sérii odborných článkov Asociácie kritickej infraštruktúry Slovenskej republiky, v ktorej postupne predstavujeme jednotlivé základné služby uvedené v prílohe č. 1 zákona č. 367/2024 Z. z. o kritickej infraštruktúre. Po tom, ako sme sa venovali prevádzkovaniu potrubí na prepravu ropy a pohonných látok, sa dnes posúvame o krok proti prúdu k službe, ktorá stojí úplne na začiatku celého ropného reťazca: ťažbe ropy.
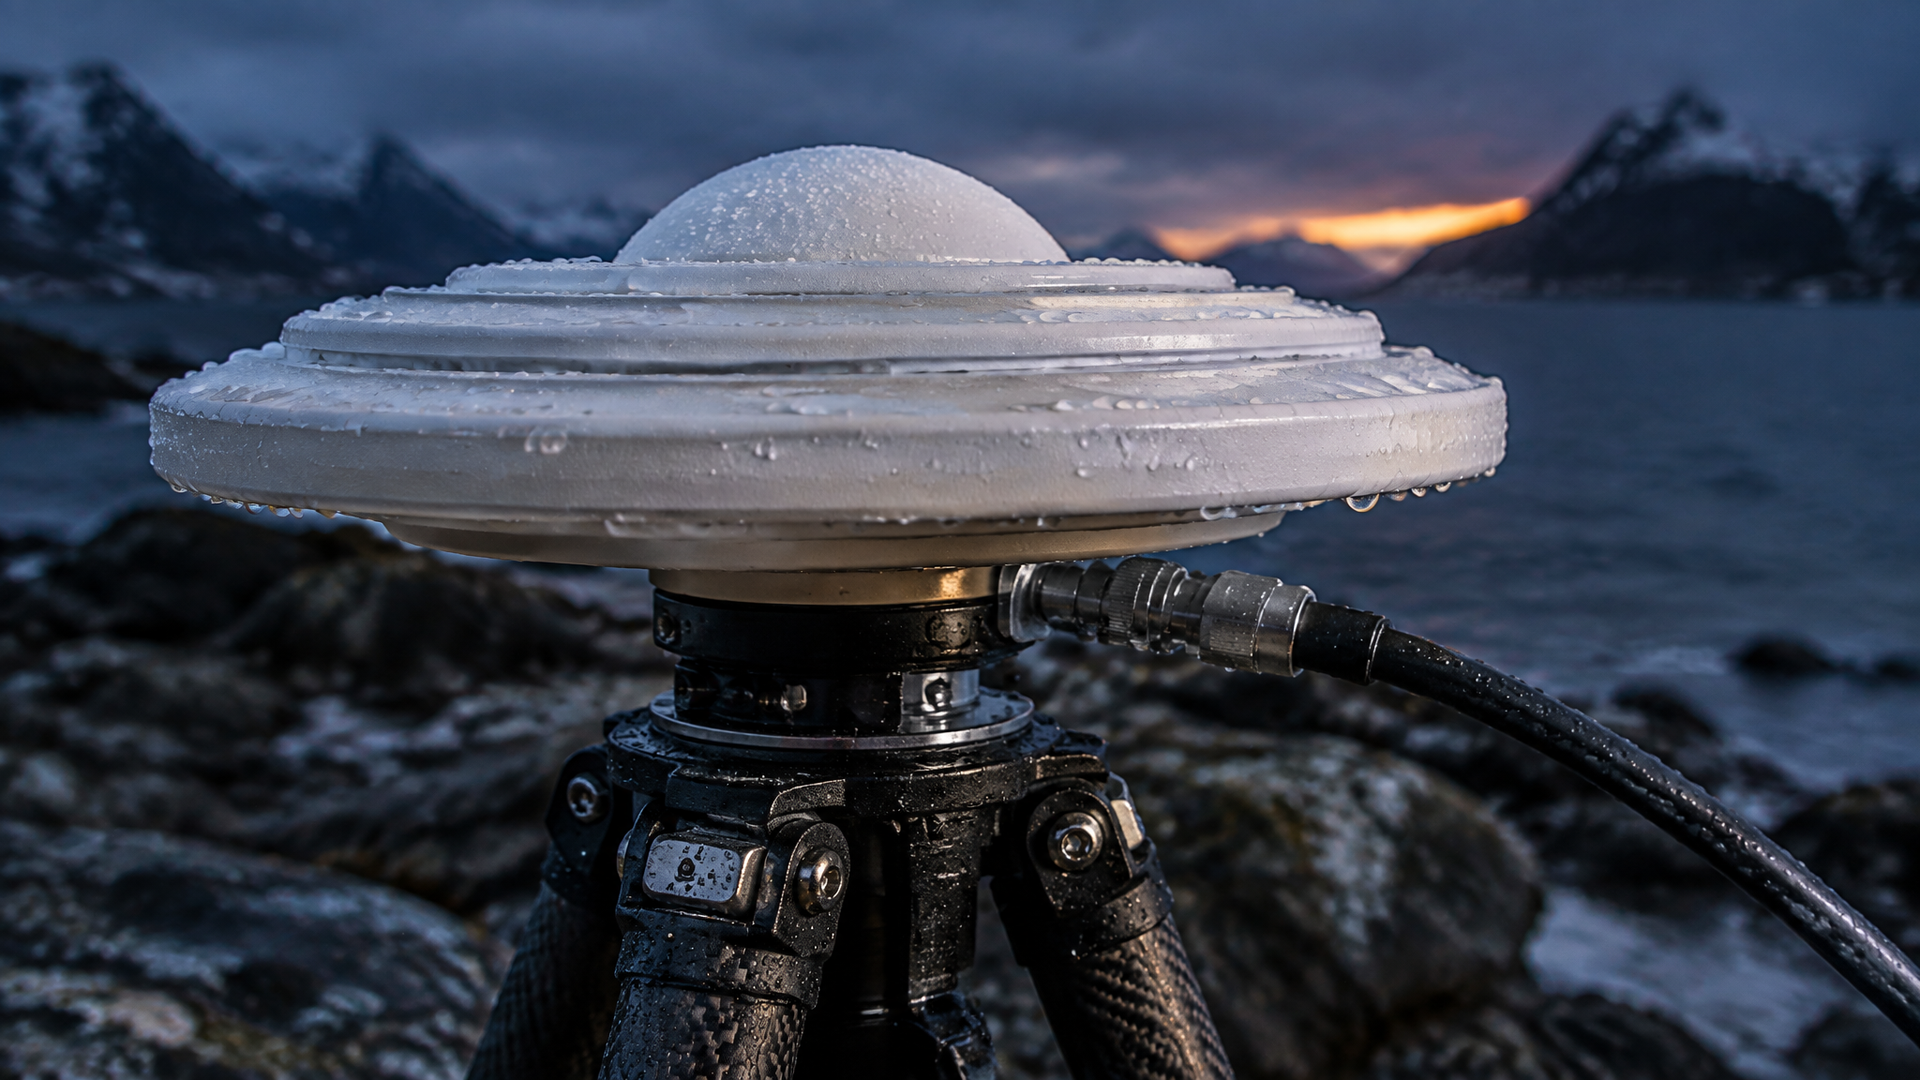
On 16 September 2026, a test carried out in Norway demonstrated a new dimension of satellite navigation security. Europe’s Galileo system was tested under so-called spoofing conditions — a situation in which a receiver is fed a fake signal and may therefore receive incorrect information about its position.
16. septembra 2026 sa v Nórsku uskutočnil test, ktorý ukázal nový rozmer bezpečnosti satelitnej navigácie. Európsky systém Galileo bol testovaný v podmienkach tzv. Spoofingu, teda situácie, pri ktorej je prijímaču podstrčený falošný signál a ten môže dostať nesprávnu informáciu o svojej polohe.